State Bank of India has told affected customers by email and WhatsApp that their personal data was found exposed on the dark web, days after disclosing the incident to stock exchanges. SBI said 3,897 customer records containing names, phone numbers, addresses and loan details were identified, and that account balances and funds remain safe.
What SBI’s regulatory filing said
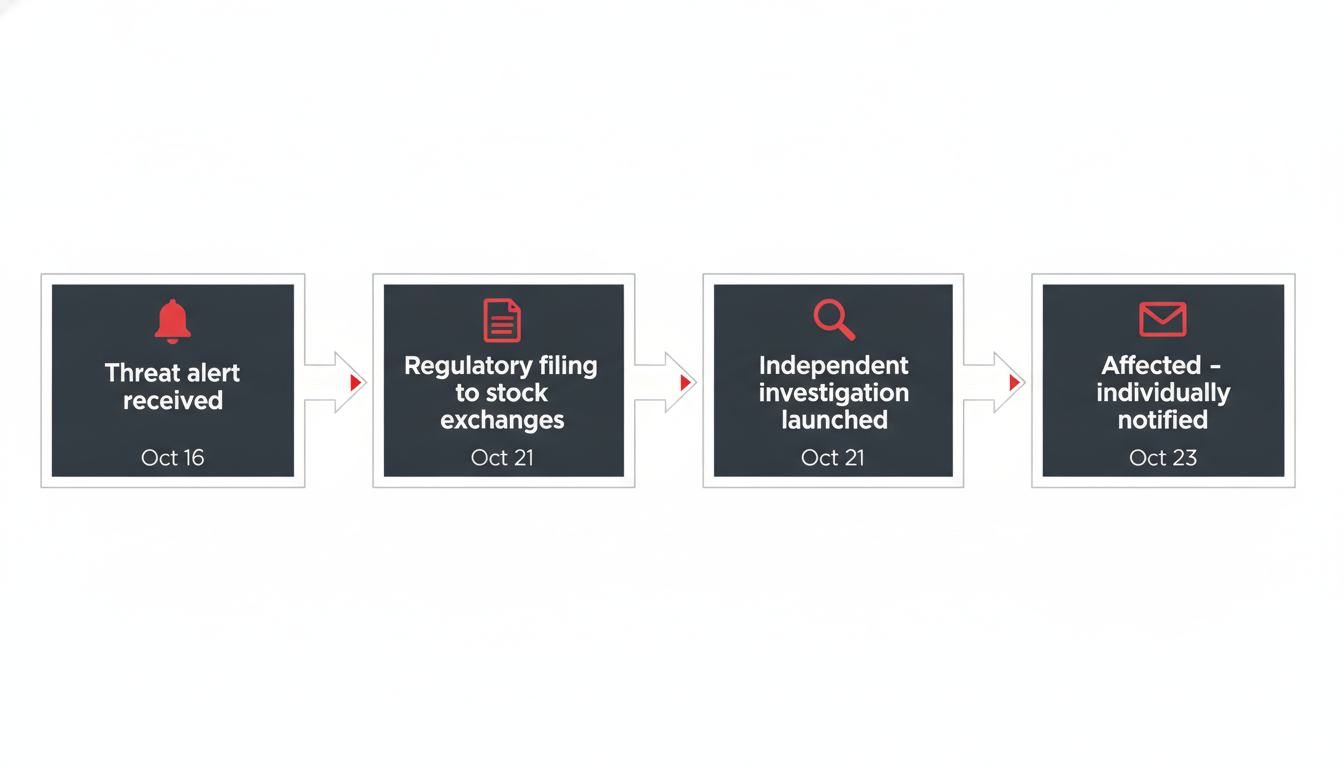
SBI disclosed to the BSE and NSE on October 21 under Regulation 30 of the SEBI Listing Obligations and Disclosure Requirements rules, in a filing titled “Incident involving Data Loss.” The bank said it learned of the exposure on October 16 through alerts from its threat intelligence vendor, the Defence Cyber Agency, and the Indian Computer Emergency Response Team, CERT-In, after the data had already surfaced on the dark web.
A preliminary review covered roughly 3.75 lakh records found online, of which SBI identified 3,897 customer records containing personally identifiable information. The bank has not said how the data left its systems, or whether the breach originated in SBI’s own infrastructure or a third party’s. It has engaged an independent cybersecurity agency empanelled by CERT-In to investigate, and says the incident has no material impact on its core business operations, financial performance or business continuity.
What data was exposed
The exposed fields include customer names, registered mobile numbers, dates of birth, gender, email and residential addresses, branch and CIF identifiers, lead IDs and loan-related details, according to SBI’s filing. The bank has said passwords, PINs and OTPs were not among the exposed fields, and that no customer funds were stolen.
SBI has also not confirmed whether the data is complete or authentic, or how far the exposure extends beyond the 3,897 records it has flagged so far. A threat actor using the name Siriusim claimed responsibility for the leak on social media on October 16, before SBI’s filing, though the claim has not been independently verified.
This is not the first Indian bank data exposure this year. Customer data and internal documents from Bank of Baroda were reportedly leaked on the dark web in July 2026. The Reserve Bank of India has repeatedly warned lenders about cybersecurity gaps that could affect financial stability, most recently in its March 2026 advisory urging banks to tighten monitoring and disclosure practices.
Why customers were not told first
The Internet Freedom Foundation pointed out that SBI’s October 21 filing told stock exchanges about the leak but did not say whether a single affected customer had been informed. The digital rights group wrote to SBI asking it to notify every affected customer directly, and copied the Reserve Bank of India and CERT-In on the letter.
Indian law does not yet require banks to notify individuals in a breach of this kind. The Digital Personal Data Protection Act’s notification provision, Section 8(6), does not take effect until May 2027. A March 2026 RBI advisory recommends that lenders notify affected customers, but that advisory is not binding.
What SBI told affected customers
Scroll.in reported on October 23 that SBI said it had individually informed affected customers by email or WhatsApp, following the Internet Freedom Foundation’s criticism. The bank told customers their account balances and funds were safe, and advised them not to share their OTP, PIN or password with anyone.
SBI has separately described the number of affected customers as “a very very small number” relative to its overall customer base, which runs into several hundred million accounts. The bank has not published a standalone press release or advisory page for the incident; its customer outreach so far has been through direct messages and a social media statement, not a dedicated notice on its website.
Frequently asked questions
Were my SBI account funds affected?
SBI says no customer funds were stolen and that account balances are safe. The exposed fields are personal identity details such as names, phone numbers, addresses and loan information, not passwords or transaction credentials.
How do I know if my data was among the 3,897 records?
SBI has said it is individually contacting affected customers by email or WhatsApp. The bank has not published a public lookup tool, and customers who have not received a message from SBI directly have not been identified as affected so far.
What should affected customers do?
SBI has advised customers not to share their OTP, PIN or password with anyone, including callers claiming to be from the bank. Security researchers have separately warned that the exposed details could be used for targeted phishing or impersonation attempts.
What to watch next
The independent cybersecurity agency’s investigation into how the data was exposed is still underway, and SBI has not given a timeline for its findings. The Internet Freedom Foundation’s letter to the RBI and CERT-In has not yet drawn a public response from either body.
Leave a Reply